GovWare 2026

Agentic speed, human approval. See Resolve live at Booth J37.

13–15 Oct · Sands Expo, SingaporeSee details

AgentRuntime protection · Agentic module

Agentic WAF,built for live traffic

Monitor production traffic, block attacks in real time, generate WAF rules from conversation, and share live probe context with SAST, DAST, and Resolve automatically.

  • Live traffic monitoring
  • AI rule generator
  • Virtual patching
  • Multi-domain WAF
Agentic WAF · FlowContext → Axiler Resolve
Traffic
WAF
App
Blocked
Shared context
ML + rules
Dual detection engines
5+
Threat intel sources
Real time
Logs and investigations
Agent sync
Shared probe context

Capabilities

What Agentic WAF does

Log report

Every request, inspectable down to the probe

Filter attack traffic by type, country, and status. Open any row to inspect HTTP details, ML confidence, client origin, and matched attack classification without leaving the WAF console.

  • Attack type and country breakdowns
  • Request log with attack, status, and path
  • Request inspection with ML confidence and client context
Agentic WAF · Log reportContext → Axiler Resolve
Live requests
Log report
Request detail
Attack type
Country
Investigations

Triage incidents with context your team can act on

Work from a prioritized queue with severity, status, and event counts. Assign owners, review attack timelines, pull threat intel, and push to Jira or Slack from the same investigation view.

  • Triage queue with severity and status filters
  • Incident detail, assignment, and attack timeline
  • Jira tickets, Slack alerts, and downloadable reports
Agentic WAF · InvestigationsContext → Axiler Resolve
Alert
Triage queue
Assign owner
Jira · Slack
Threat intel
Report

AI rule generator

Talk to your WAF. Deploy rules from the conversation.

Describe what you want to block in plain language. The AI rule generator turns intent into deployable WAF policy without hand-writing rules or guessing syntax.

  • Natural-language rule creation
  • Review and deploy from one workflow
  • Faster response when routes are under probe
Agentic WAF · AI rule generatorContext → Axiler Resolve
Prompt
AI rule
Review
Deploy
Scope
Traffic preview

Virtual patching

Block zero-days at the edge while engineering ships the fix

When a new exploit hits production, deploy a virtual patch on the WAF in minutes. Traffic stays protected at the edge while your team validates and merges the permanent code fix.

  • Rapid edge mitigation without waiting on deploy cycles
  • Scoped rules tied to the vulnerable route or parameter
  • Coordinate with investigations and AI rule generator
Agentic WAF · Virtual patchingContext → Axiler Resolve
Exploit
Virtual patch
Edge blocked
Code fix PR
Patch retired

Agentic context

Live probes become shared context for every agent

When WAF sees an attack on a route, DAST knows where to retest, Resolve knows what to rank, and the rest of the suite acts on the same signal, not a disconnected block list.

  • Probe context shared across the AppSec Suite
  • Correlated findings in Axiler Resolve
  • Human approval before ranked remediation
Agentic WAF · Agentic contextContext → Axiler Resolve
Live probe
WAF
Agentic Code Analysis
Agentic DAST
Resolve

WAF + SAST correlation

Correlate live probes to code fixes and remediate on both ends

Connect Agentic WAF with Agentic Code Analysis and a runtime probe becomes a code-level investigation. Block the attack at the edge, trace it to the files that matter, review the AI-generated fix, and open a PR without losing the production context that started the work.

Runtime remediation

Virtual patches and generated WAF rules protect the vulnerable route while engineering reviews the fix. Traffic stays blocked at the edge from the moment the probe is confirmed.

Code remediation

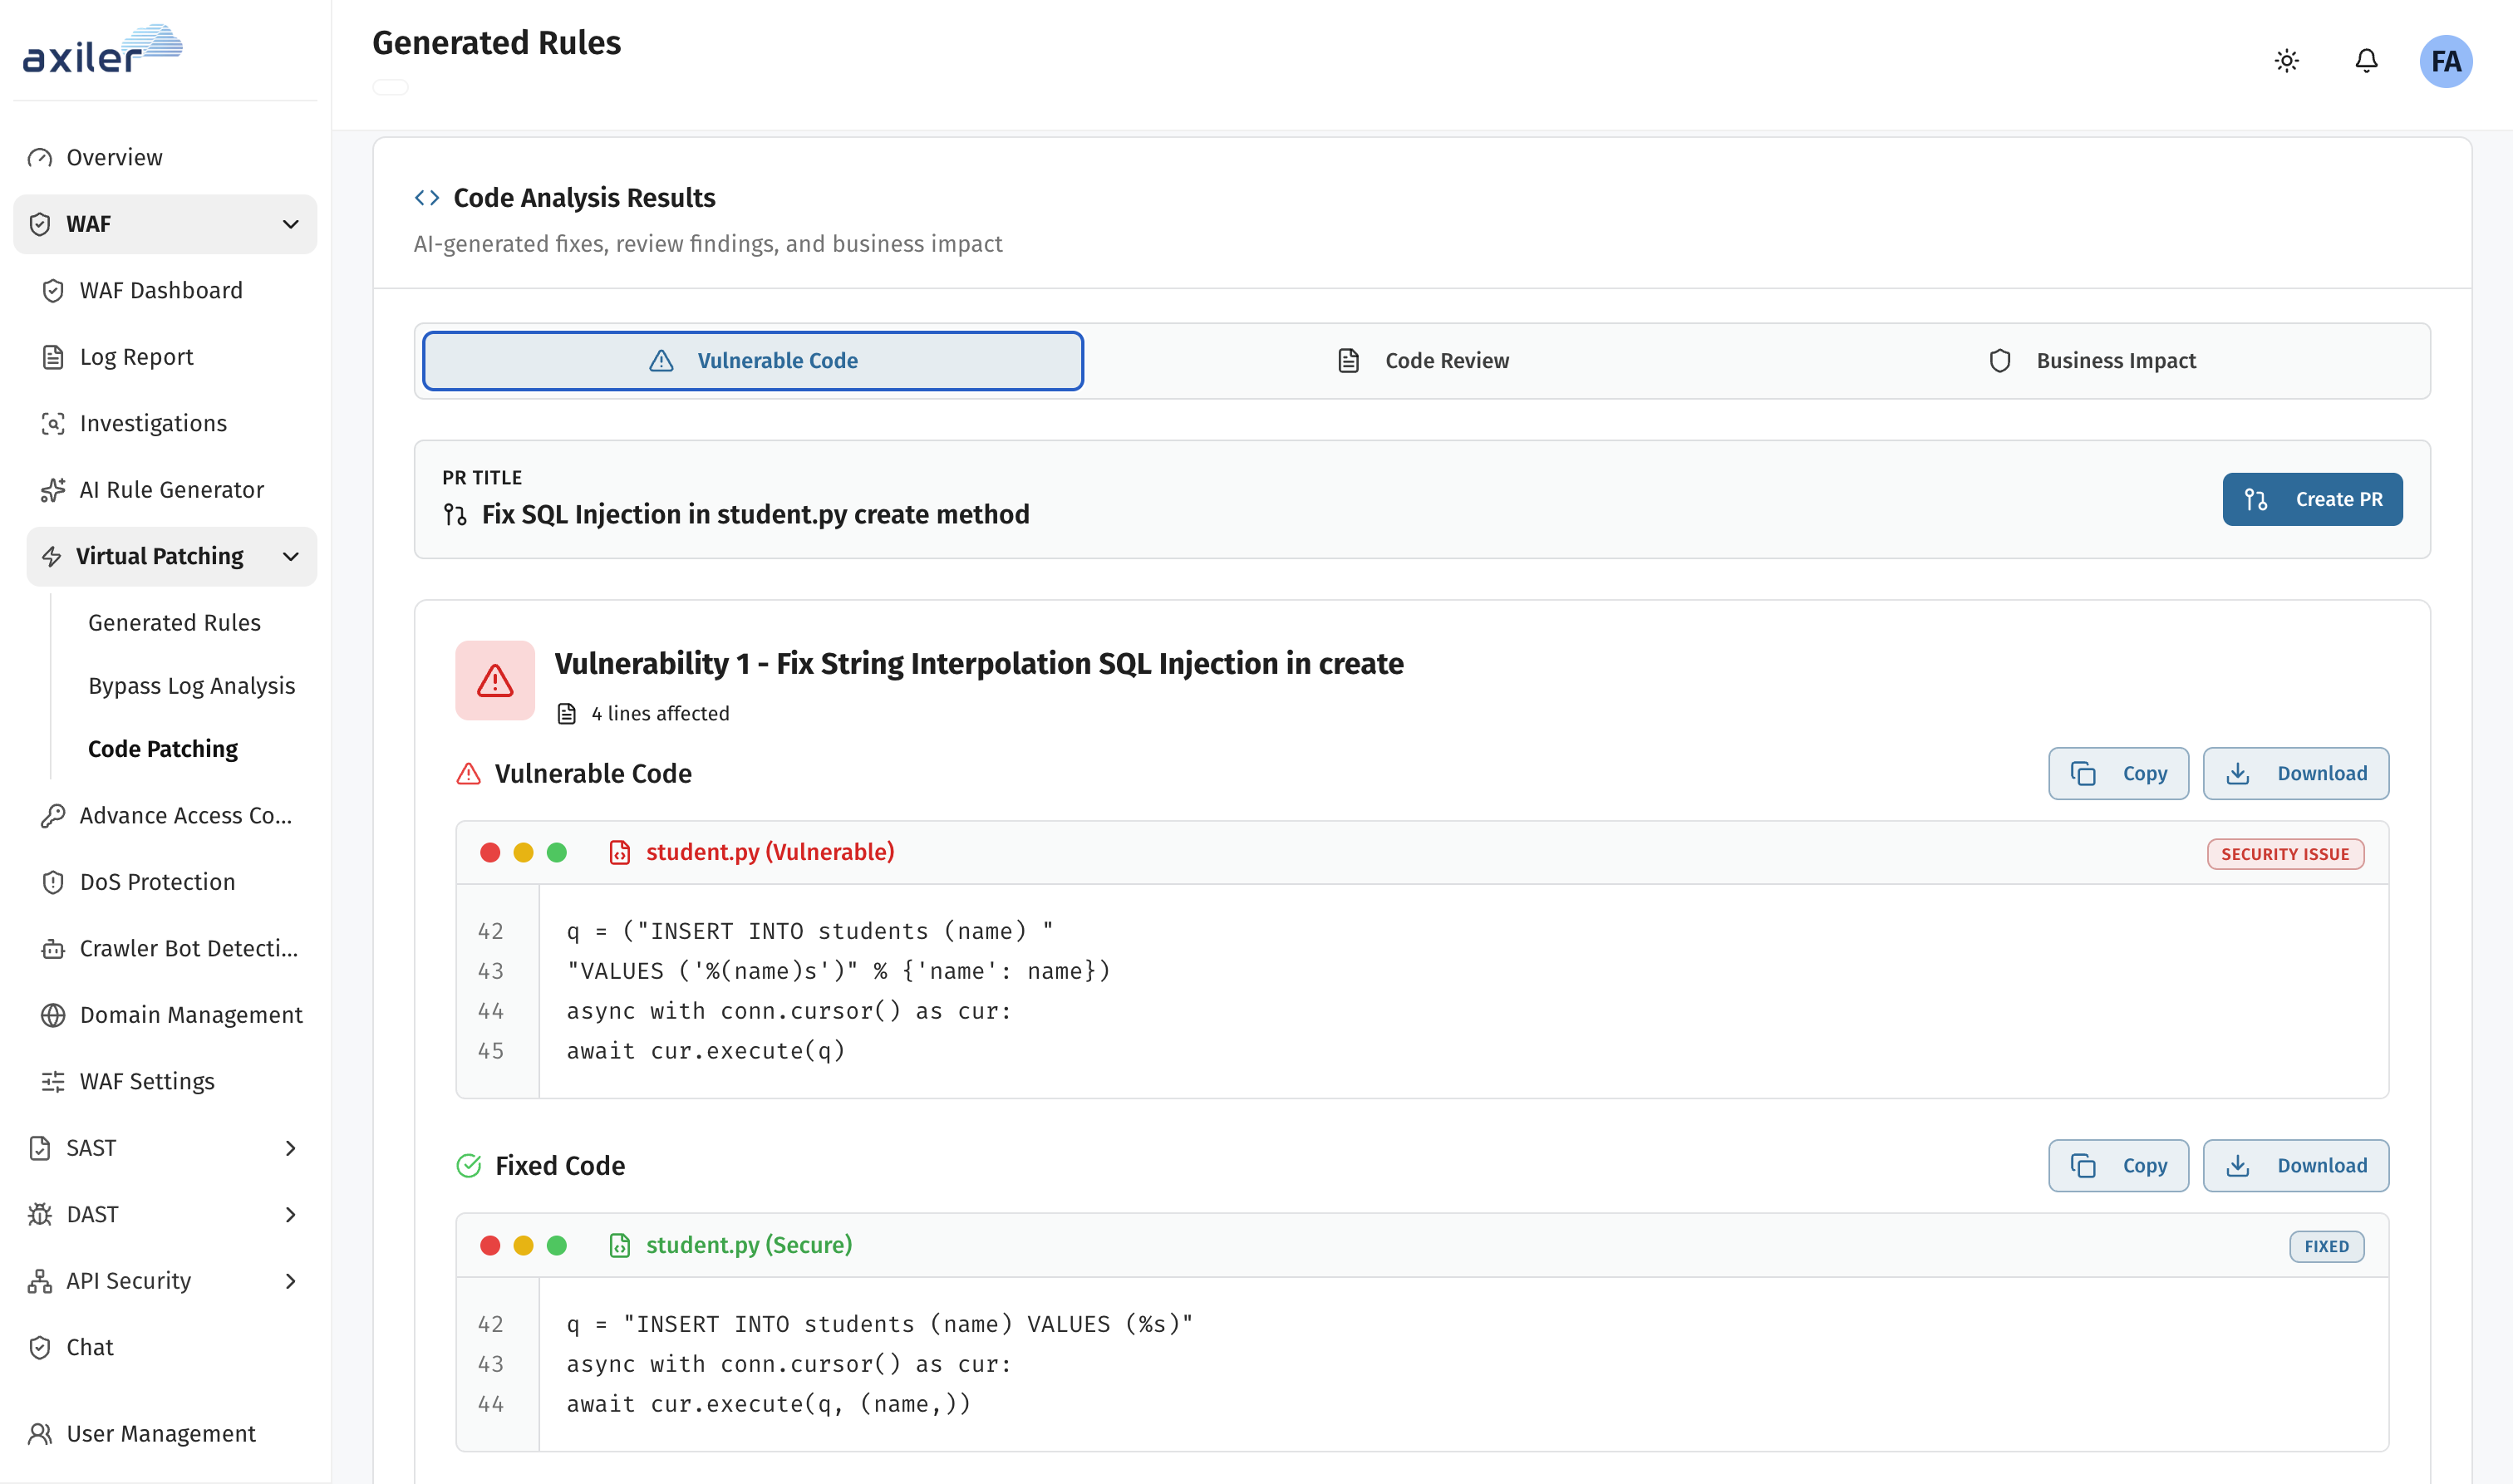
Agentic Code Analysis maps the attack parameter to relevant source files, surfaces vulnerable vs fixed code, and lets you create a PR from the same correlated workflow.

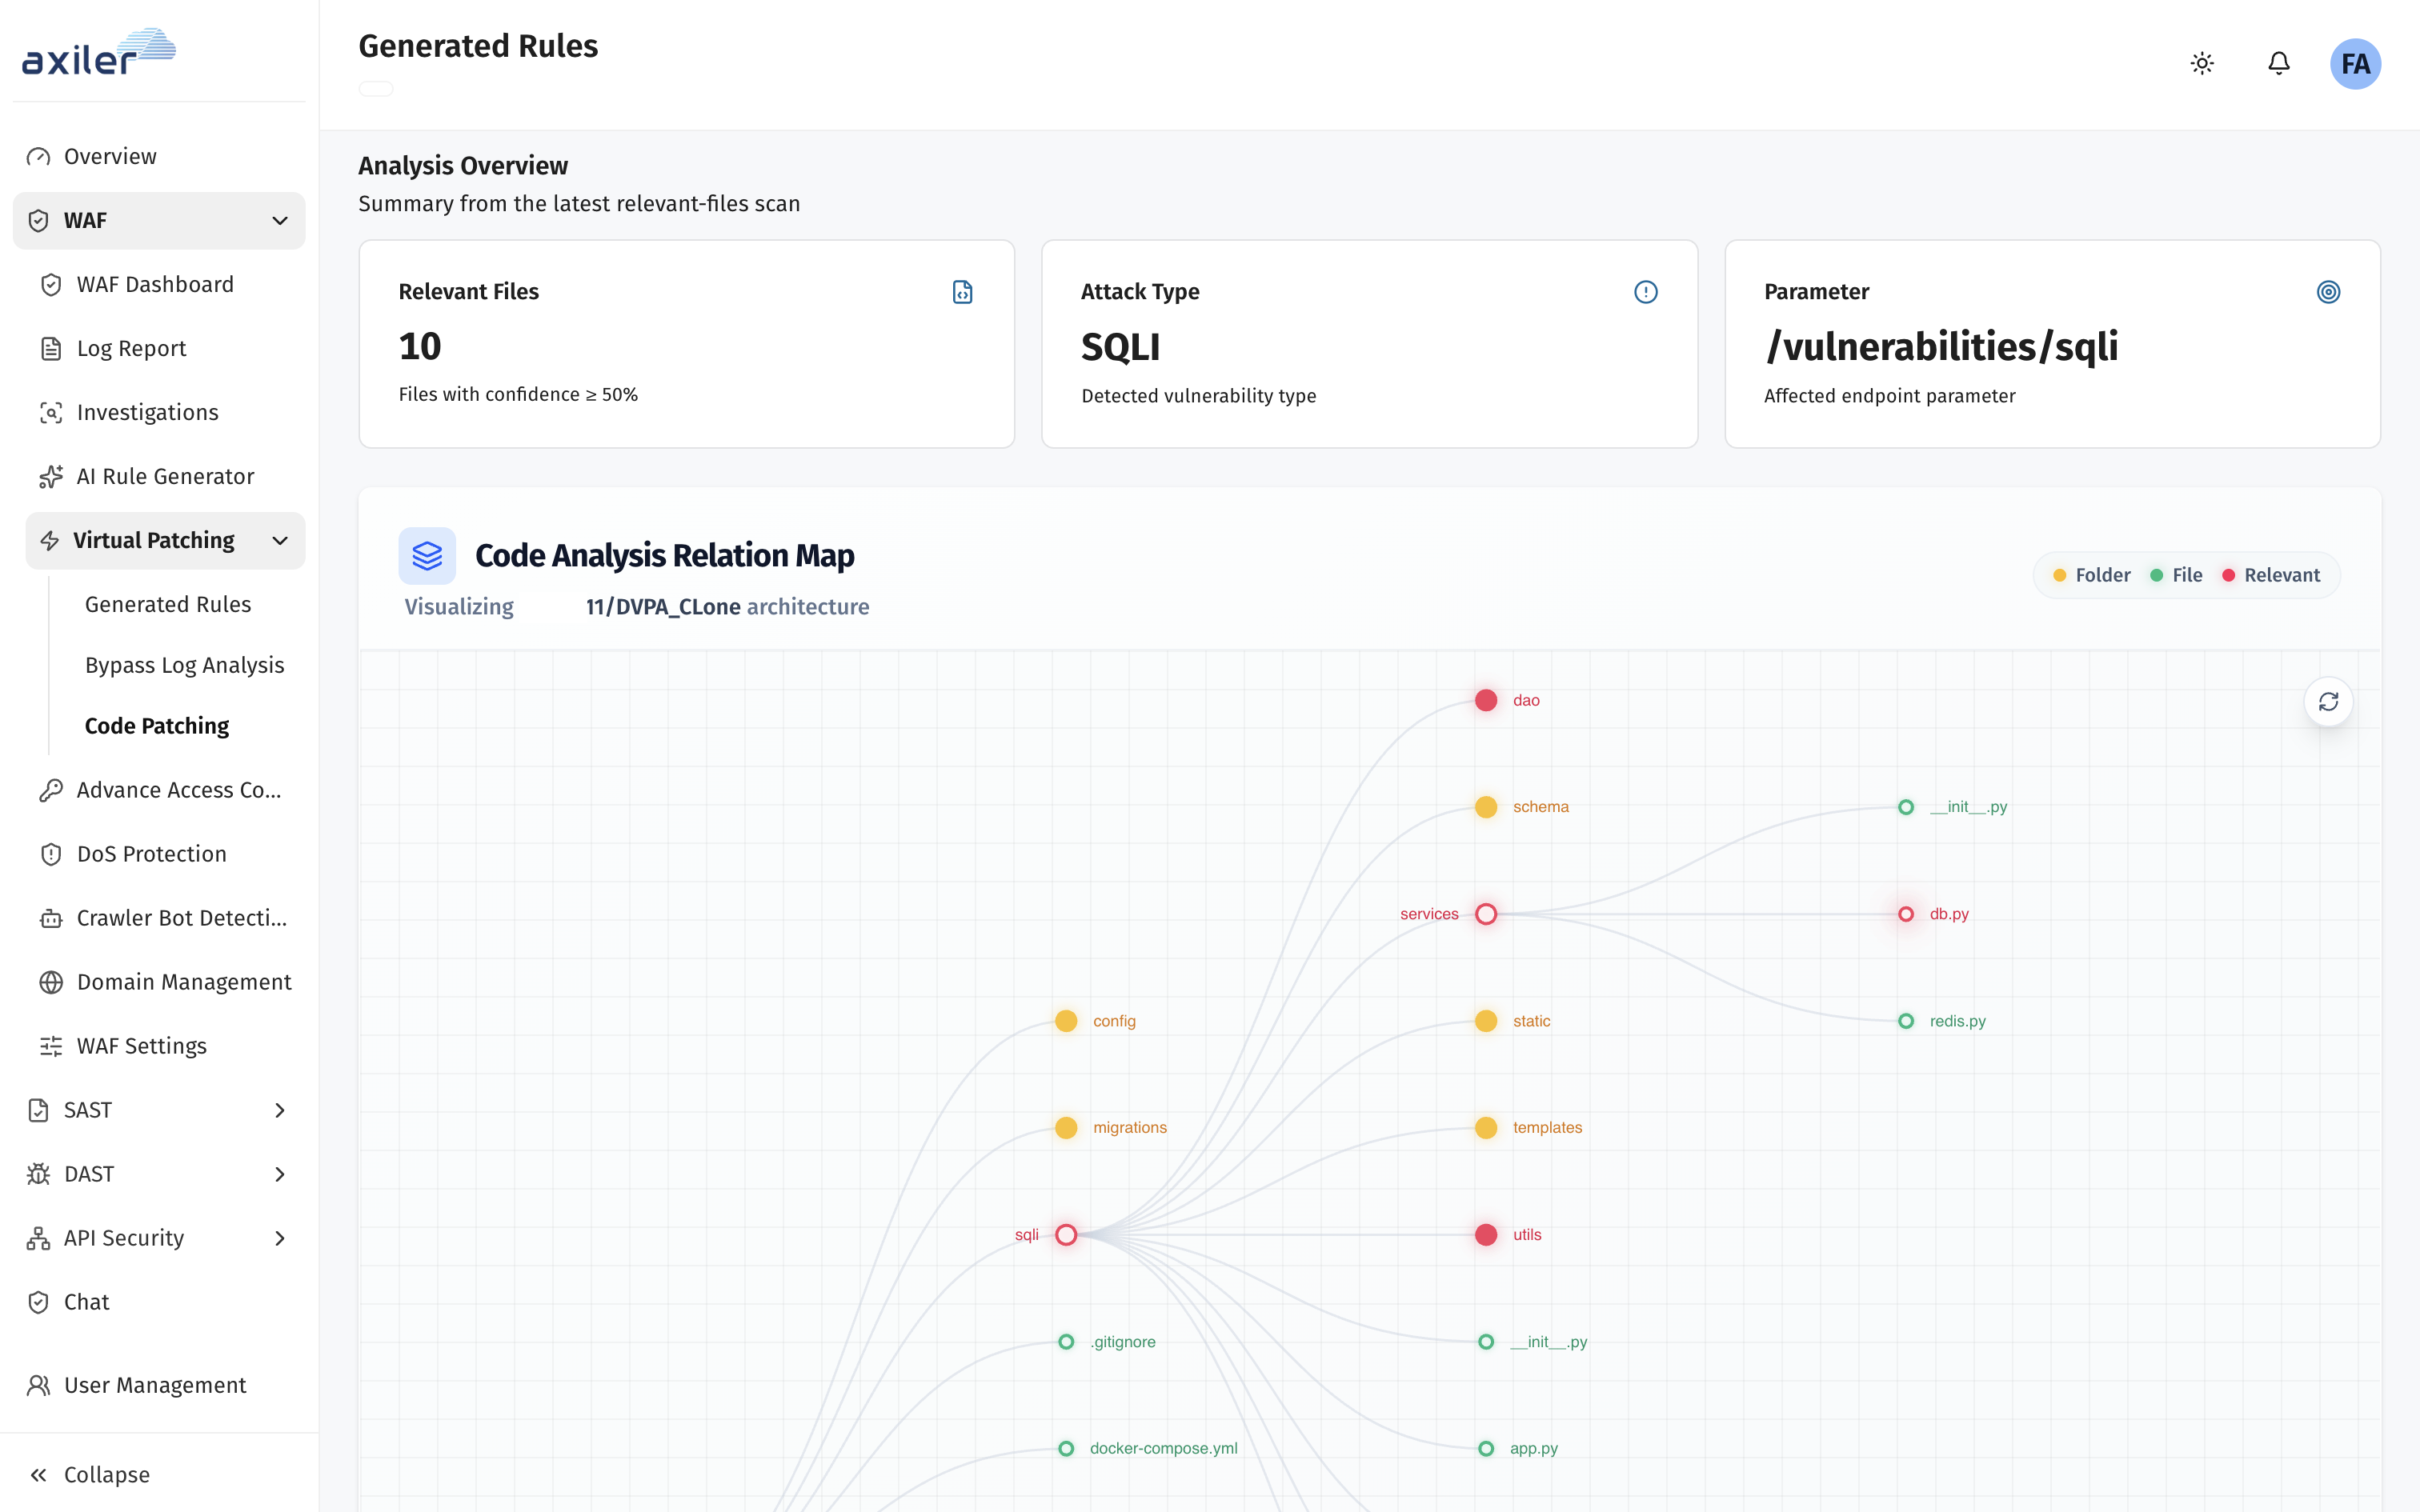
Map the probe to source files

A SQL injection hit on /vulnerabilities/sqli is traced through your repo. The relation map highlights sqli, dao, services, and utils, the paths Agentic Code Analysis should prioritize.

Code analysis results showing vulnerable and fixed SQL injection code with Create PR action

Review the fix and deploy to code

See vulnerable and patched code side by side, validate business impact, then create a pull request. The WAF probe that triggered the work stays linked through the entire review.

Generated rules relation map linking a SQL injection WAF probe to relevant source files in the codebase

Available only when Agentic Code Analysis is connected to your WAF workspace.

Explore Agentic Code Analysis

Crawler & bot detection

Block AI crawlers from scraping your content

Stop GPTBot, ClaudeBot, and other AI training crawlers from harvesting your pages while still allowing search engines and monitoring bots you trust. Agentic WAF classifies automation at the edge so content stays yours.

  • Block known AI scraper user-agents and suspicious crawl patterns
  • Allow legitimate search and uptime bots with fine-grained rules
  • Log blocked crawler traffic alongside other WAF events

Blocked

  • GPTBot
  • ClaudeBot
  • CCBot
  • Bytespider
  • Amazonbot

Allowed

  • Googlebot
  • Bingbot
  • Uptime monitors

Runtime coverage

Block OWASP-style attacks on autopilot

  • Injection and abuse

    Stop SQL injection, XSS, and command-style payloads before they reach your apps and APIs.

  • DoS and rate limiting

    Protect endpoints from floods, brute force, and abusive traffic patterns with configurable limits.

  • Bots and crawlers

    Separate malicious automation from legitimate crawlers with bot management controls.

  • Access control

    Block or allow by IP, path, geo, user-agent, and directory with advanced access policies.

  • Virtual patching

    Mitigate zero-days at the edge while engineering ships the code fix.

  • Domain and SSL ops

    Manage multiple domains, certificates, and SSL refresh from the same WAF console.

AppSec Suite

WAF is one agent in a connected stack

Agentic WAF shares live attack signals with Agentic Code Analysis, DAST, API Security, and Cloud Security. Axiler Resolve ranks what matters. Your team approves once, then fixes with full context.

Let's talk

Protect your web apps
with Athena.

See it on your stack in a 30-minute live demo. No slides, just your data.

  • 30 minLive demo on your stack
  • ReviewCode findings with context
  • SOC 2Type II certified